
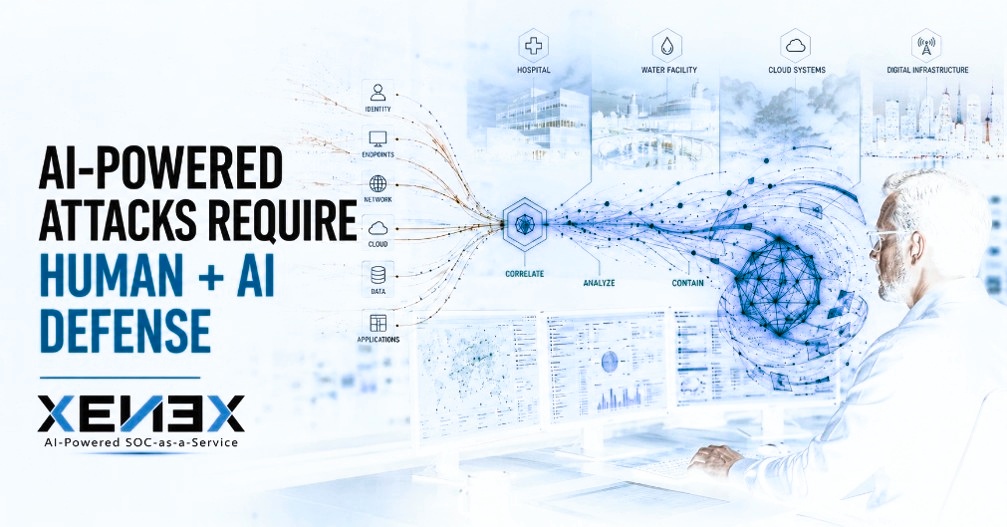
AI is changing the cybersecurity landscape. Organizations must act now to prepare for a new generation of cyber threats.
More than 100 technology and cybersecurity organizations have issued an urgent warning about the growing threat of AI-enabled cyberattacks. The message is clear: attackers are gaining new capabilities and moving faster than traditional security teams can respond.
For CEOs, CISOs, and IT leaders, this creates an important question: Is your cybersecurity strategy ready for AI-powered attacks?
The warning, reported by Axios, highlights the need for stronger defenses. Organizations must improve their visibility, close security gaps, and respond to threats faster.
At XeneX SOC, we believe this requires a new approach to security operations. Organizations need more than additional security tools; they need a continuously operating security capability that combines AI-driven analysis with experienced human expertise.
That is exactly what XeneX delivers.
XeneX Was Built for the AI Cybersecurity Era
Many organizations already have security tools in place. However, those tools often operate independently, creating gaps in visibility and making it harder to identify threats across multiple systems.
Meanwhile, attackers are using AI to increase their speed and scale. Traditional security teams cannot keep up by manually reviewing every alert.
XeneX addresses this challenge through a managed Agentic SOC. We combine purpose-built AI, security auto
mation, and experienced analysts to protect your organization 24/7/365.
Our approach helps you:
Detect suspicious activity faster.
Investigate threats across your environment.
Prioritize the risks that matter most.
Respond to threats with greater speed.
Maintain human oversight and accountability.
You gain the benefits of advanced AI security without having to build and operate your own SOC.
XeneX does not sell its platform as a standalone product. We deliver the complete security operation as a managed service, supported by OnePortal for unified service delivery, governance, and security visibility.
How the Industry Warning Validates the XeneX Approach
The warning reinforces several principles that guide our security operations. These principles help organizations prepare for increasingly sophisticated cyber threats.
1. AI-Powered Attacks Require AI-Powered Defense
Attackers are using AI to accelerate reconnaissance, discover vulnerabilities, and automate malicious activity. As a result, security teams must respond with greater speed and precision.
Traditional security operations often depend on analysts manually reviewing alerts. This approach becomes increasingly difficult as event volumes grow.
XeneX uses purpose-built AI to analyze security telemetry, correlate activity, and prioritize potential threats. Our AI also supports investigations and helps accelerate response.
Experienced security analysts validate important findings and oversee consequential actions. You get the speed of AI with the accountability of experienced cybersecurity professionals.
2. Advanced Security Must Be Accessible to More Organizations
Large enterprises often have dedicated security teams and substantial cybersecurity budgets. Small and midsized organizations face many of the same threats, but they may lack the resources to build an enterprise-grade SOC.
This creates a dangerous security gap. Organizations need access to advanced security capabilities without the cost and complexity of building an internal operation.
XeneX closes that gap by delivering managed security operations as a service. You gain access to continuous monitoring, advanced threat detection, and experienced security professionals without having to hire a full team of analysts.
This makes advanced cybersecurity more accessible to organizations with limited resources. You can strengthen your defenses while allowing your IT team to focus on business priorities.
3. More Security Tools Will Not Solve the Problem
Most organizations already use multiple security products. These may include endpoint protection, email security, identity management, firewalls, cloud security, and vulnerability management.
The challenge is connecting these technologies. When security tools operate in silos, important threats can go unnoticed.
XeneX brings security telemetry together through a vendor-neutral architecture. We collect and normalize data across your approved environment, allowing our AI to correlate events and identify suspicious activity.
OnePortal brings cases, evidence, workflows, risks, and reporting into a unified service experience. You gain better visibility without having to replace your existing security investments.
4. Focus on the Risks That Matter Most
Not every vulnerability creates the same level of risk. A long list of security findings does not necessarily tell you where to act first.
Organizations need to understand which weaknesses could lead to significant business impact. This requires connecting technical findings with business priorities.
XeneX helps connect security findings with assets, identities, attack paths, and business context. This gives your team better information when evaluating potential threats.
Instead of focusing only on the number of alerts or vulnerabilities, you can prioritize the exposures that matter most. The objective is simple: reduce meaningful cyber risk.
5. Continuous Monitoring Must Replace Periodic Reassurance
Cyber threats do not follow a business schedule. An annual security assessment can identify weaknesses, but it cannot provide continuous protection against threats that emerge tomorrow.
XeneX delivers 24/7/365 security monitoring. Our team continuously monitors your environment, investigates suspicious activity, and helps address emerging risks.
This approach also supports compliance readiness and incident preparedness. You gain ongoing visibility into your security operations rather than relying solely on periodic assessments.
XeneX can also help provide the documentation and reporting needed for governance, audits, and cyber-insurance discussions. These capabilities support compliance efforts, but they do not automatically guarantee compliance, certification, or insurance coverage.
6. Agentic AI Must Remain Accountable
AI agents can perform increasingly complex tasks. However, autonomous security operations must remain governed and accountable.
Organizations need to understand what their AI agents can access and which actions they can perform. They also need visibility into how those agents operate.
Important questions include:
Which AI agent performed an action?
What identity and permissions did it use?
Which systems or data did it access?
Was the action authorized?
Can the action be stopped or investigated?
These questions become even more important as organizations adopt autonomous digital workers. Security leaders must maintain control while taking advantage of AI-driven automation.
XeneX combines AI-driven automation with human oversight and governed response workflows. Our approach is designed to accelerate security operations while maintaining accountability.
The goal is not AI without oversight. It is AI that helps your security team work faster and more effectively.
How to Prepare for AI-Powered Cyberattacks
The industry warning makes one thing clear: organizations should not wait until AI-enabled attacks become routine. You can begin strengthening your defenses today.
Here are seven practical steps to consider.
1. Identify Your Most Critical Business Risks
Start by identifying the systems, data, and services that matter most to your organization. Understand what could happen if those assets were compromised.
This helps you focus security investments on the areas with the greatest potential business impact. It also provides a foundation for prioritizing remediation.
2. Close Dangerous Security Gaps
Review identity permissions, exposed systems, vulnerabilities, and security configurations. Prioritize weaknesses that could create a path to significant business disruption.
Regular assessments can help identify these gaps. Continuous monitoring helps you understand when new risks emerge.
3. Establish Continuous Security Visibility
Make sure your security team can monitor activity across endpoints, networks, cloud environments, identities, and email. Disconnected tools can leave important gaps in your security coverage.
A unified security operation helps connect activity across your environment. This improves your ability to identify suspicious behavior and investigate potential threats.
4. Use AI to Improve Defensive Speed
Apply AI to security analysis, event correlation, investigation, and response. This helps your team process more information and focus on meaningful threats.
AI-driven security operations can also reduce the burden of repetitive tasks. Your analysts can spend more time addressing complex risks and supporting business resilience.
5. Maintain Human Oversight
Automation can accelerate security operations. However, consequential decisions require appropriate oversight, accountability, and business context.
Establish clear policies for AI-driven actions. Make sure your security team understands when automation can act independently and when human approval is required.
6. Test Your Response and Recovery Capabilities
Do not assume your organization can recover from a cyberattack. Test incident response procedures, containment capabilities, and backup recovery.
Regular exercises help identify weaknesses before an actual incident exposes them. They also help your team understand its responsibilities during a crisis.
7. Measure Security Outcomes
Security effectiveness should be measured by more than the number of alerts processed. Evaluate detection speed, response time, risk reduction, operational resilience, and remediation effectiveness.
These measurements help demonstrate the business value of your cybersecurity investments. They also provide a clearer picture of how well your security operation protects your organization.
The Future of Cybersecurity Is Human + AI
The industry warning reinforces an important reality. AI-powered attacks require a more advanced approach to cybersecurity.
Organizations need greater visibility, faster analysis, and more effective response capabilities. However, technology alone is not enough.
You also need experienced security professionals who understand your environment, assess business impact, and maintain accountability. This combination is essential for effective security operations.
That is the model behind XeneX SOC. Our managed Agentic SOC combines purpose-built AI, specialized AI agents, security automation, and experienced analysts.
Together, these capabilities help you reduce cyber risk, improve response times, and simplify security operations. You gain access to advanced cybersecurity without the cost and complexity of building your own SOC.
The industry warning is not a formal endorsement of XeneX SOC. However, it reinforces the need for the operating model we have developed.
AI-powered attacks demand AI-powered defense. And that defense must be available, accountable, and continuously operating.
Prepare Your Organization for the Next Generation of Cyber Threats
The time to strengthen your cybersecurity operations is now. XeneX SOC helps organizations improve their security posture through continuous monitoring, AI-driven threat detection, and experienced human expertise.
You do not need to manage another security platform or build an internal SOC from scratch. You need a security partner that can help you protect what matters.
See What an Agentic SOC Can Do for Your Organization
Discover how XeneX combines AI automation and human expertise to deliver 24/7/365 cybersecurity protection. Our team can help you understand how an Agentic SOC fits your security strategy.